01
Identities & roles
Access adapted to responsibilities and scopes.
SECURITY & RELIABILITY
Controlled access, ongoing supervision and protective practices built into every layer of the platform.
Access, responsibilities and continuity must support teams while remaining proportionate to the real context of each location.
Controlled access · preserved context · defined continuity
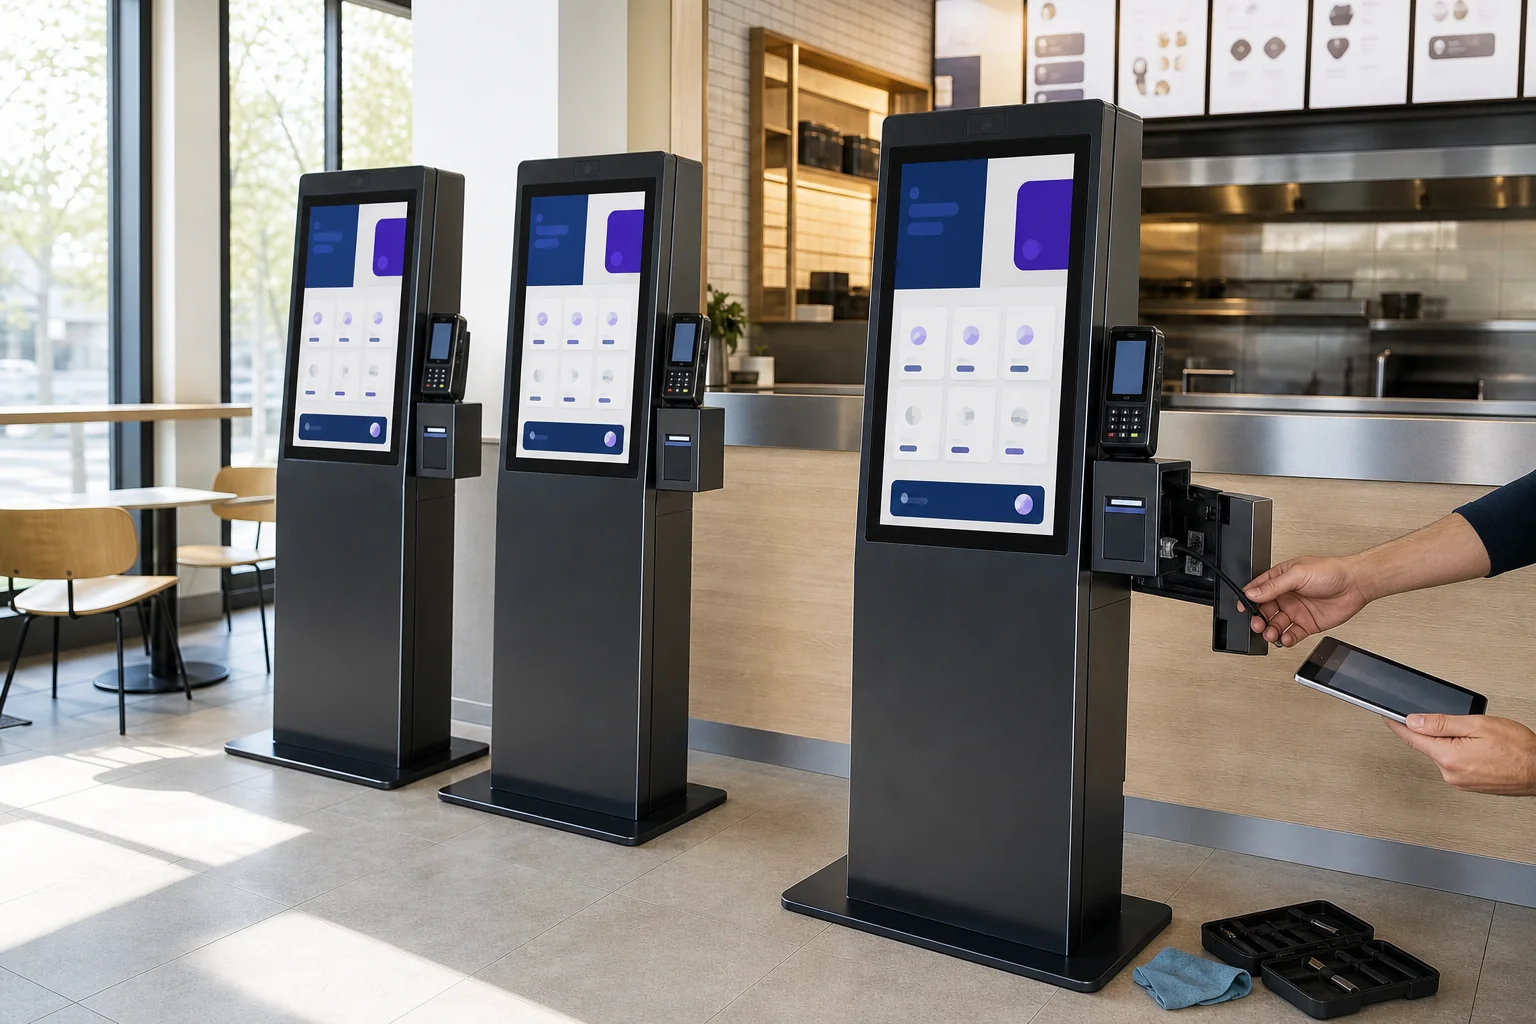 Illustrative scenario
All wording remains proportionate to the evidence available. No certification or quantified availability is shown without validated documentation.
Access adapted to responsibilities and scopes.
Practices to be specified in validated documentation.
Events that authorised teams can understand.
Responsibilities and channels to be confirmed contractually.
Users, permissions and local practices to be defined.
Practices, supervision and documentation to be validated.
Scopes and commitments specific to each service.
No public documentation has been provided. This area will remain empty until validation.
To be documentedNo dedicated address has been provided. Use the general form without including sensitive information.
Contact TYTAN ONEHardware, software, transactions, data and action share the same context—within the scope that has actually been validated.
Modules avoid recreating conflicting definitions.
Peaks, errors and responsibilities remain visible.
Every role sees the level of information it needs.
The scope can evolve once dependencies have been assessed.
Short, honest answers proportionate to the actual scope.
No certification is published on this site because no validated documentation has been provided. Evidence will be added only after confirmation.
Tell us about your operation. We will help identify the first useful scope.
Request a demo